AI · Service AI security review and prompt-injection testing

An adversarial review of AI agents and LLM features: prompt-injection testing, tool permission boundaries, data leakage paths, and a written report with fixes.

In short

Prompt injection is when text an AI system reads — a web page, a document, an email — contains instructions that the model follows as if they came from its operator. An AI security review tests how your system behaves under that attack and others like it. We review the permissions each tool holds, attempt injection through every channel the model reads, and report what an attacker could actually reach.
How to engage
Security review
Practice
AI
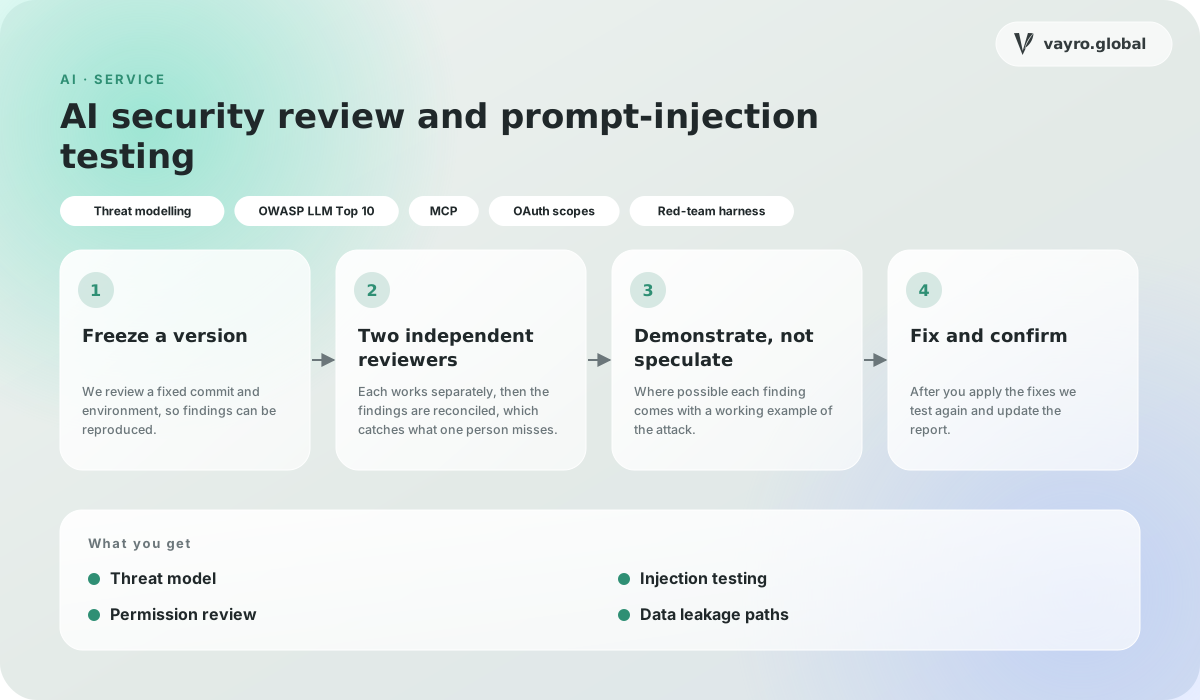
AI security review and prompt-injection testing — how Vayro delivers it: Freeze a version, then Two independent reviewers, then Demonstrate, not speculate, then Fix and confirm. Includes threat model, injection testing, permission review, data leakage paths.
When you need it

Signs this is the right service

  • An agent is about to be given tools that write, send or pay.
  • The system reads content you do not control: customer messages, uploaded files, web pages.
  • An enterprise customer's security team has sent a questionnaire about your AI features.
  • An AI feature shipped quickly and nobody has tried to break it.
What's included

What you get

Threat model

What the system can reach, who can put text in front of it, and what the worst outcome of each path would be.

Injection testing

Direct and indirect prompt-injection attempts through every input channel, including tool results and retrieved documents.

Permission review

Each tool's scope checked against what the task needs, with read and write paths separated and high-impact actions gated.

Data leakage paths

Whether one user's or tenant's data can reach another, through retrieval, memory, logs or tool output.

Report and re-review

Findings ranked by impact with a concrete fix for each, and a second pass once the fixes are in.

How we deliver it

The process

  1. 01

    Freeze a version

    We review a fixed commit and environment, so findings can be reproduced.

  2. 02

    Two independent reviewers

    Each works separately, then the findings are reconciled, which catches what one person misses.

  3. 03

    Demonstrate, not speculate

    Where possible each finding comes with a working example of the attack.

  4. 04

    Fix and confirm

    After you apply the fixes we test again and update the report.

Threat modellingOWASP LLM Top 10MCPOAuth scopesRed-team harness
Questions

AI & LLM security review: common questions

Can prompt injection be fully prevented?

Not by filtering text. Instruction-shaped content will reach the model sooner or later. What holds is limiting what the model can do: if it has no permission to call a tool, no injected instruction can make it call that tool.

What do we get at the end?

A written report listing each finding, how serious it is, how to reproduce it and how to fix it, followed by a re-review after the fixes.

Do you need access to production?

No. A staging environment that matches production, plus the code and configuration, is enough for most reviews and is safer.

Is this the same as a penetration test?

It overlaps but is not the same. A penetration test looks at your infrastructure and application in general. This review focuses on the risks that come from a model reading untrusted text and acting on it.
06 / Let’s build

Bring us the difficult problem.

01

New projects

A paragraph about the problem is enough to start. We reply within two working days, usually with questions rather than a quote.

support@vayro.global
02

Careers

Engineers, designers and researchers who like systems that are hard to get right. Send something you built and what you would change about it now.

support@vayro.global
03

Studio

Based in India and working remotely, with overlap hours agreed up front so your team always has a time to reach us.

IST · GMT · ET overlap
04

Read

Guides on AI agents, RAG, MCP, tokenization and chain abstraction, written by the engineers who build them.

vayro.global/insights