01
New projects
A paragraph about the problem is enough to start. We reply within two working days, usually with questions rather than a quote.
A line-by-line adversarial review of Solidity and Rust contracts by two independent reviewers, with a ranked findings report, fixes, and a re-review included.
A smart contract security review (often called an audit) is a line-by-line examination of contract code by engineers looking for ways to steal funds, freeze them, or break the contract's rules. Two of our reviewers read the code independently, combine their findings, and deliver a report that ranks each issue and explains how to fix it. A second review after your fixes is included.
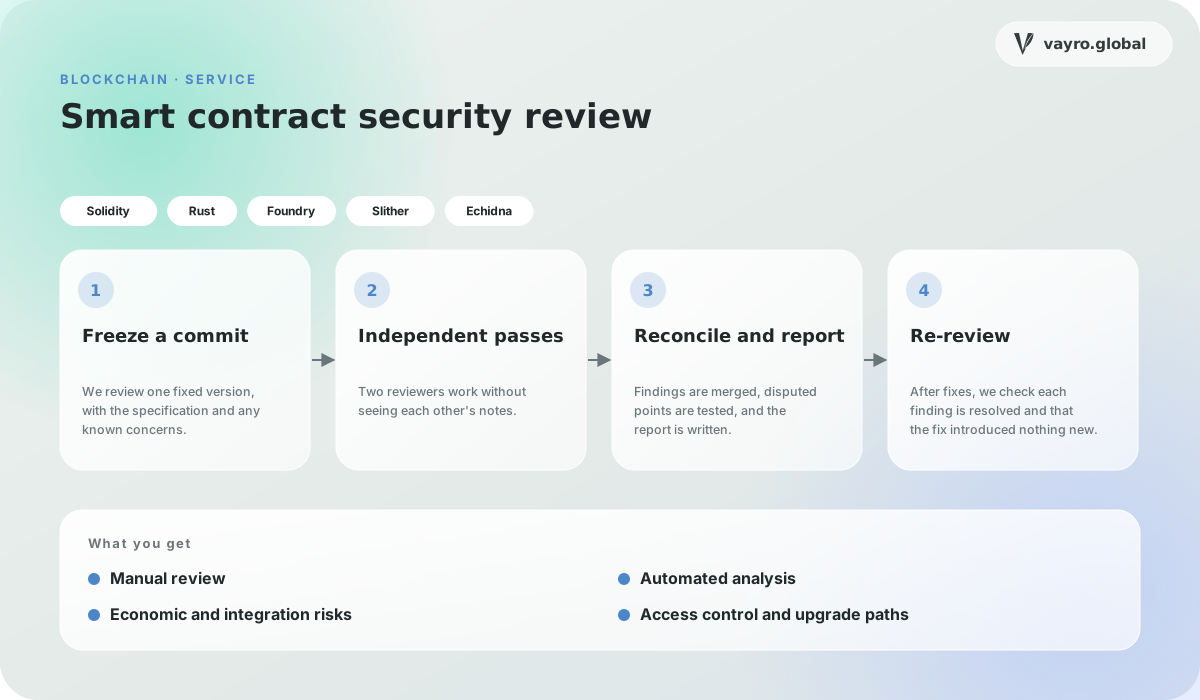
Every line read by two reviewers working separately, focused on logic errors that tools cannot find.
Static analysis and fuzzing run alongside the manual work, with the output triaged rather than pasted into the report.
Oracle dependence, flash-loan exposure, reentrancy across contracts, and assumptions about tokens the contract interacts with.
Who can change what, with which keys, after what delay — and what happens if a key is lost or stolen.
Each finding with severity, a reproduction and a recommended fix; then a re-review of your changes.
We review one fixed version, with the specification and any known concerns.
Two reviewers work without seeing each other's notes.
Findings are merged, disputed points are tested, and the report is written.
After fixes, we check each finding is resolved and that the fix introduced nothing new.
A paragraph about the problem is enough to start. We reply within two working days, usually with questions rather than a quote.
Engineers, designers and researchers who like systems that are hard to get right. Send something you built and what you would change about it now.
Based in India and working remotely, with overlap hours agreed up front so your team always has a time to reach us.
Guides on AI agents, RAG, MCP, tokenization and chain abstraction, written by the engineers who build them.